


Cloud Security
- Click 'Security' > 'Cloud Security' to expand this group.
Cloud Security covers everything that is not an endpoint: the cloud accounts you have connected, the Kubernetes clusters you run, the container registries and code repositories you build from, and the APIs you expose. All nine pages in the group run inside one embedded cloud security console, so they share its look, its filter bars and its pagers.
You can work through the findings raised against your cloud estate, see what has been discovered, score yourself against compliance frameworks, watch what containers do at runtime, follow the tickets raised from findings, read the runtime alerts, schedule reports and inspect your API surface.
The pages in this group
| Page | Description |
| Issues | The working list of findings, with a summary tab and a rule engine. See Issues. |
| Cloud Assets | The inventory of discovered resources, with ten filters. See Cloud Assets. |
| Clusters | The onboarded Kubernetes clusters and their benchmark results. See Clusters. |
| Compliance | A score per framework, and the failed checks behind it. See Compliance. |
| Runtime Protection | What containers actually do, and the policies that constrain them. See Runtime Protection. |
| Ticket Summary | The tickets raised from findings in your connected trackers. See Ticket Summary. |
| Alerts | The runtime alert stream and the triggers that act on it. See Cloud Alerts. |
| Reports | Scheduled CWPP, CSPM and ASPM reports. See Cloud Reports. |
| API Security | Discovered API endpoints, uploaded specifications and the scans over them. See API Security. |
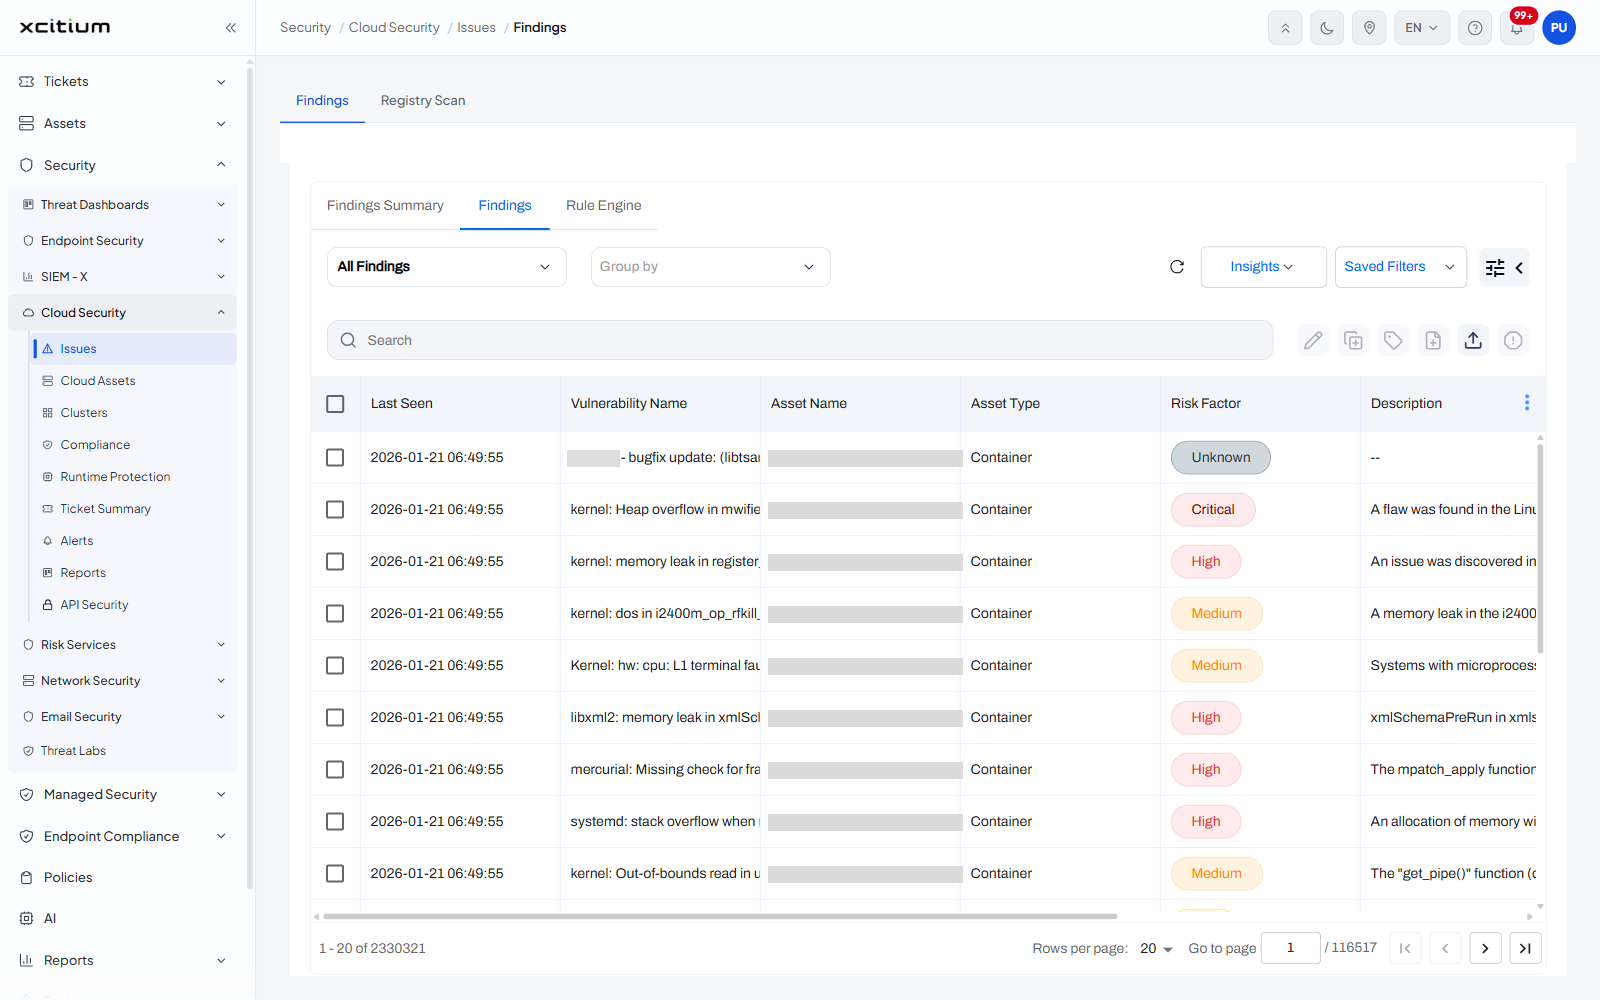
Open a Cloud Security page
- Click 'Security' in the left navigation bar.
- Click 'Cloud Security'. The group expands.
- Click the page you want.